Skip to content
Contact us

Press kit

Writing about Moatgator?

Ready-to-use descriptions, facts with their source, logos and screenshots. Everything here can be used without asking; for anything else, write to us.

Short description

About 60 words

Moatgator is a Brazilian mobile app security company. It protects Android apps that move money, with iOS (beta), against tampering, hooking, rooted devices and the overlay and remote-access techniques behind Pix fraud. Protection is added in the customer's build pipeline and the response is a policy file kept in their repository. The free Scan grades an APK, AAB or IPA without an account.

Long description

In Brazil, much of the fraud against financial apps happens on the customer's own phone: fake screens drawn over the payment screen, accessibility services that read and tap for the victim, remote-access sessions, rooted or hooked devices and repackaged copies of the app. Rules on the server do not see any of this.

Moatgator works on the device and in the build. A free Scan grades any APK, AAB or IPA against OWASP MASVS-RESILIENCE. Shield hardens the compiled app in the customer's CI and returns it unsigned, so the signing keys never leave the company. Runtime detects root, emulators, Frida, debuggers and tampering, and a versioned moatgator.yml decides the response: monitor, warn, block or end the session. Every detection starts in monitor mode, and Pulse shows the attempts in the console.

Moatgator is built by GZ Segurança e Defesa Cibernética LTDA in Cascavel, Paraná. The company is explicit about limits: no protection is absolute. The goal is to raise the cost of an attack and give the customer's team the signal and the time to respond. The website is available in 10 languages.


Facts

Each fact links to where it can be checked. Product facts point to the page of this site that states them.

Company
GZ Segurança e Defesa Cibernética LTDA, CNPJ 40.988.106/0001-60
Source · Checked on
Headquarters
Cascavel, Paraná, Brazil
Source · Checked on
What it is
Runtime protection (RASP) and hardening for mobile apps: Scan, Shield, Runtime, Attest, Pulse and Pix Shield
Source · Checked on
Platforms
Android; iOS (beta); React Native, Expo and Flutter
Source · Checked on
Free Scan
APK, AAB or IPA, graded from A to F against OWASP MASVS-RESILIENCE, no account needed
Source · Checked on
Pricing
Public prices per app; the free plan covers the first app
Source · Checked on
Signing keys
The protected app is returned unsigned; the customer signs it in their own pipeline
Source · Checked on
Website
moatgator.com, in 10 languages
Source · Checked on

Logos and mascot

SVG for print and web, PNG with a transparent background. Gus, the mascot, is for developer-facing pieces; enterprise material uses the symbol only.

Screenshots

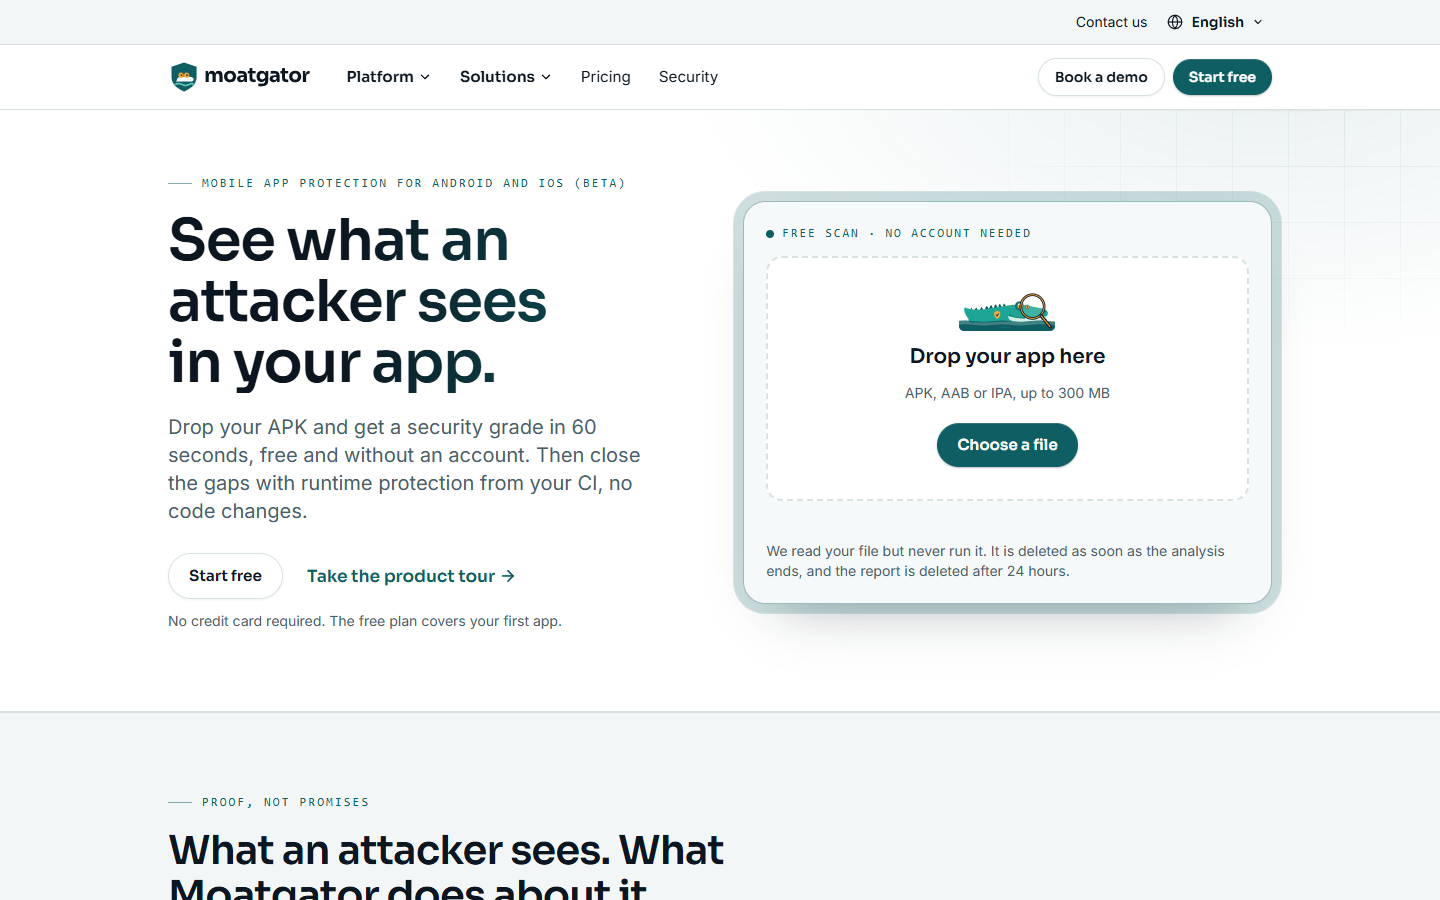
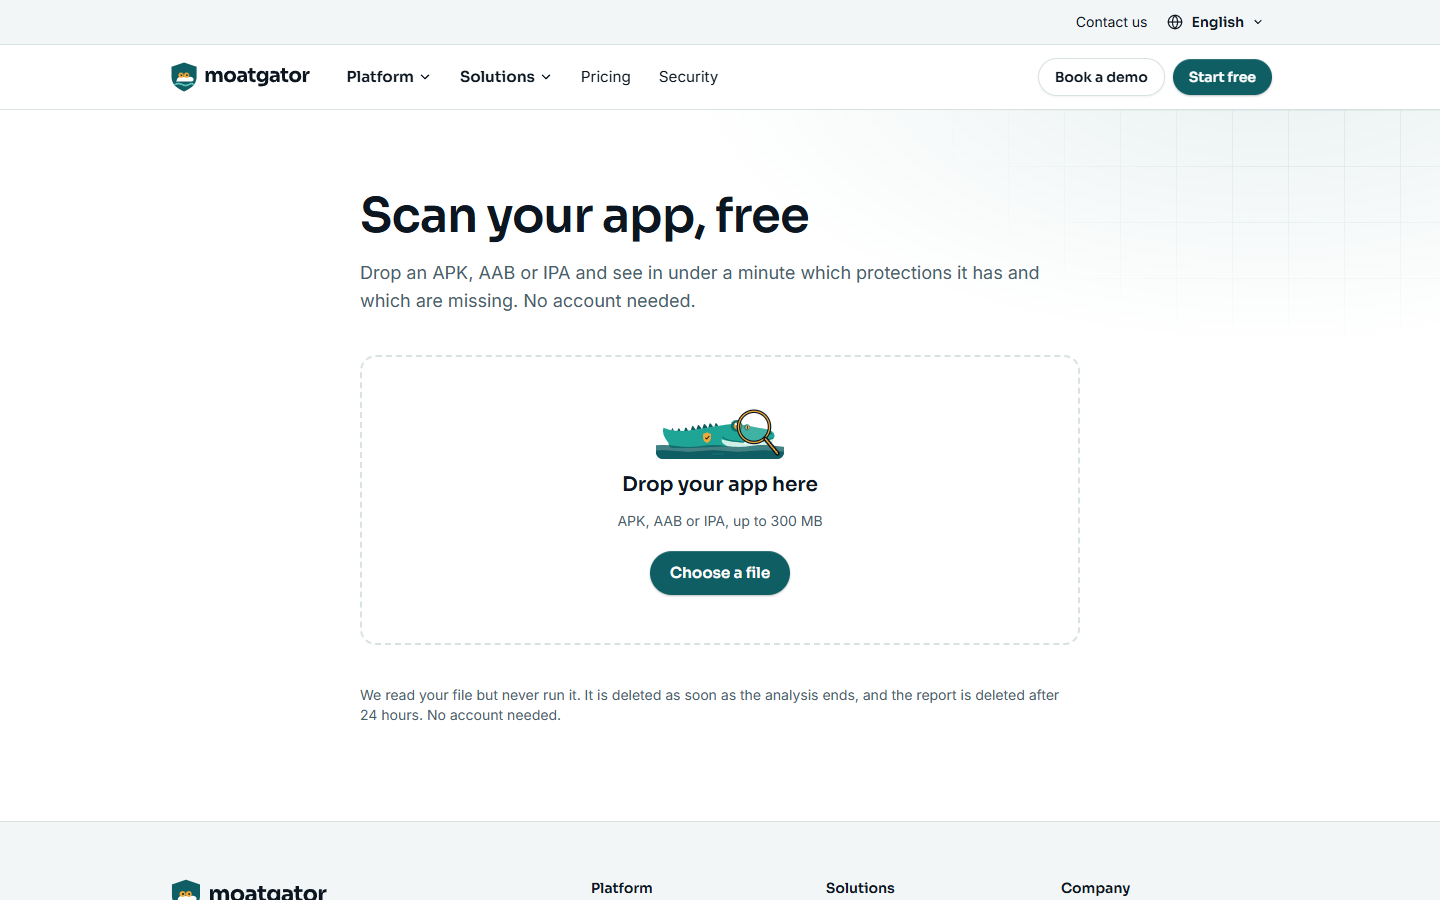
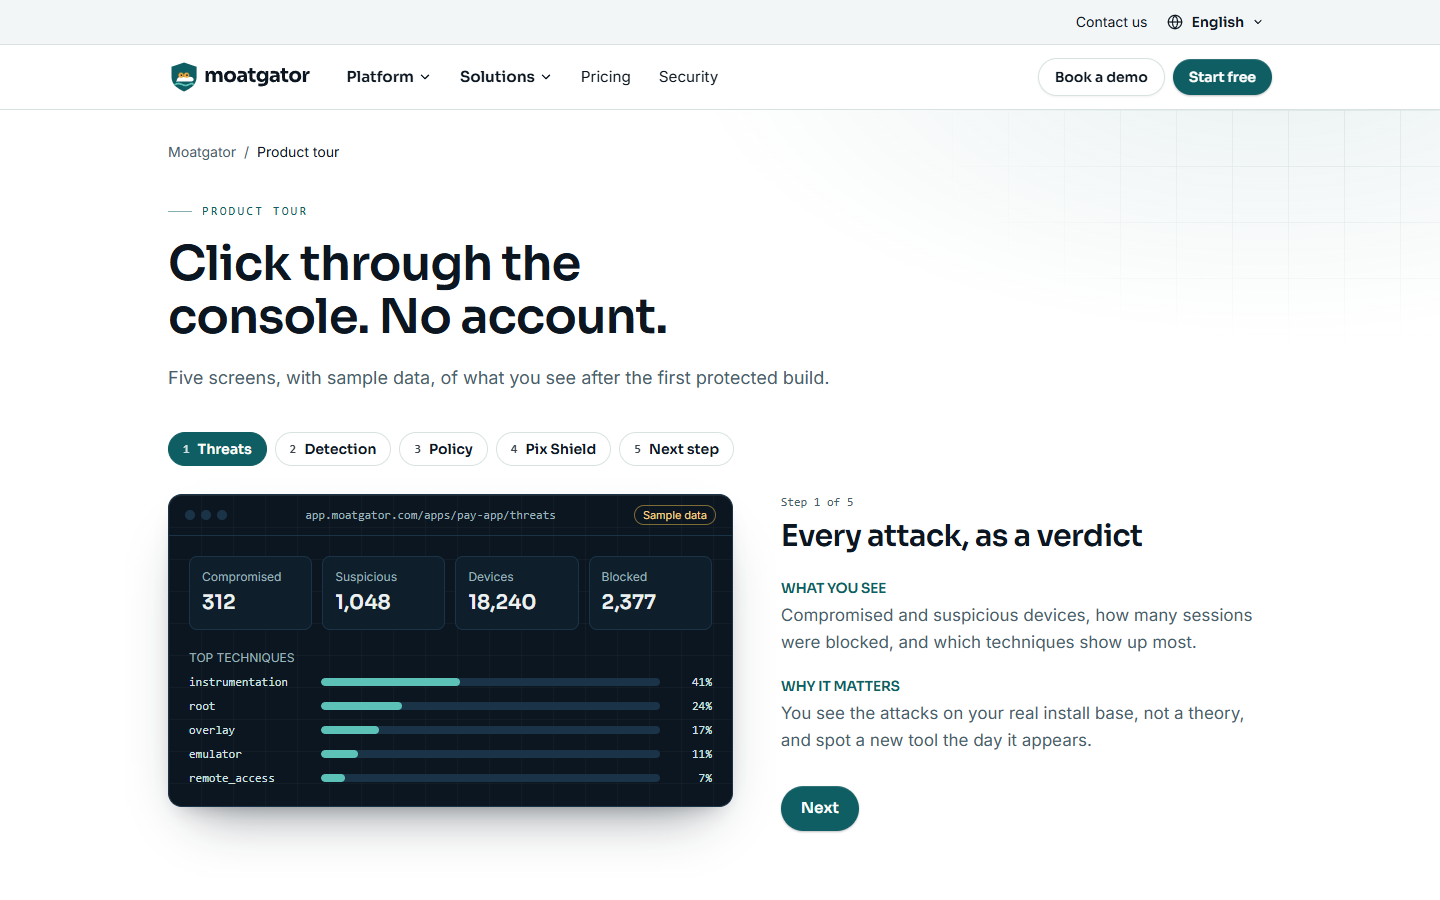
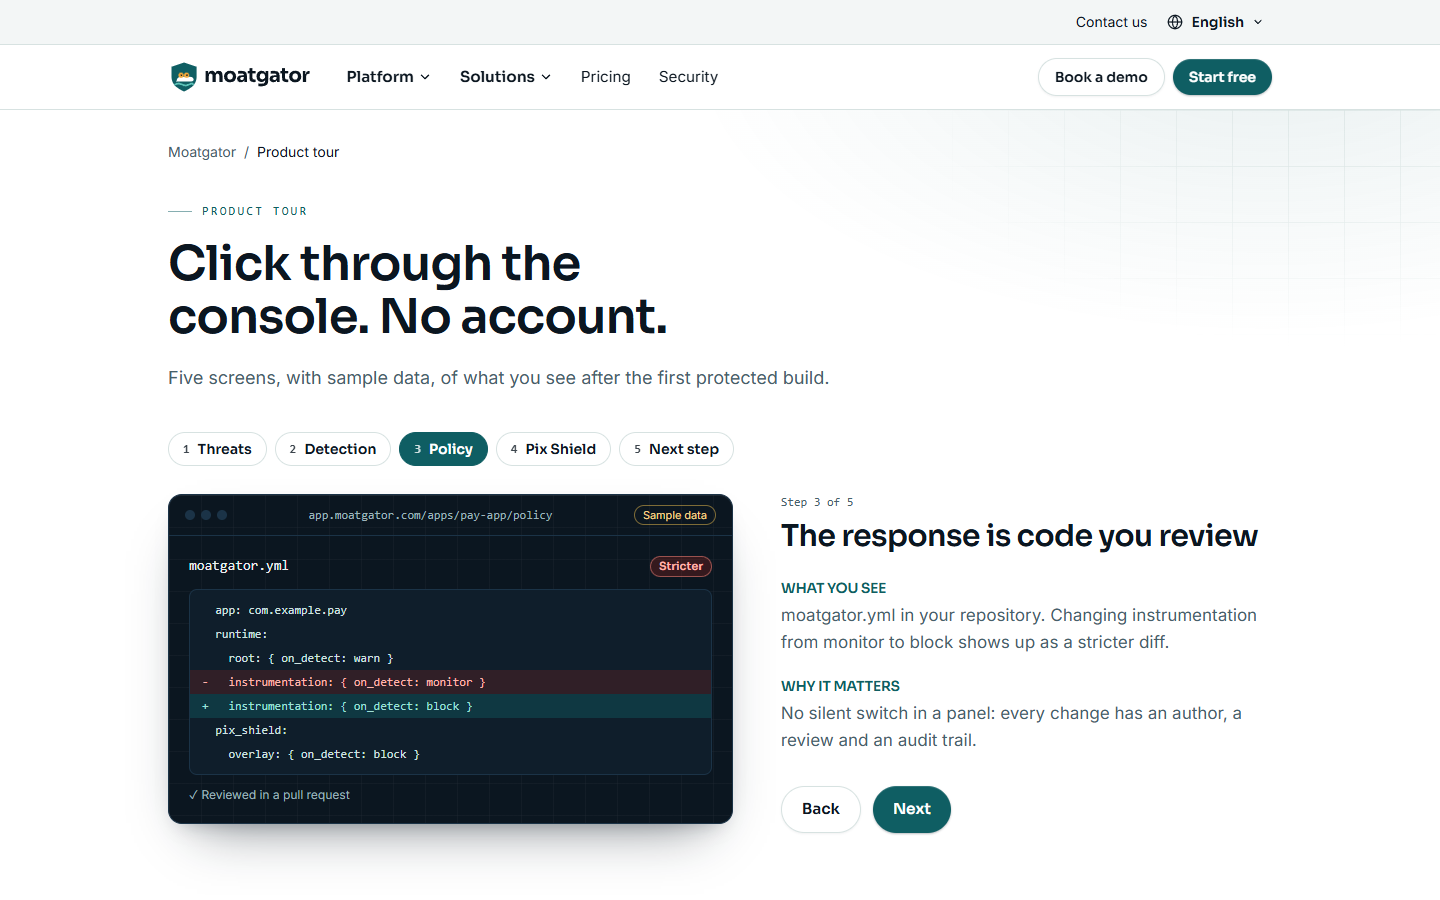
Captured from this website at 1440 × 900. The console screens come from the product tour and show labelled sample data, not customer data.

  • Moatgator home page with the free Scan upload and the headline about what an attacker sees in an app

    Home page

  • The free Scan page, where an APK, AAB or IPA is uploaded to get a protection grade

    Free Scan

  • Product tour showing the threats dashboard of the console with labelled sample data

    Console: threats

  • Product tour showing the moatgator.yml policy with a stricter change reviewed in a pull request

    Console: policy as code

Using the brand

  • Use the files as provided, without changing colors, proportions or the space around the symbol.
  • Write the name as Moatgator, with a capital M; the logo itself is lowercase.
  • Gus is calm and never shown as aggressive.
  • Please do not describe Moatgator as making an app impossible to attack: no protection is absolute, and we say so.

Press contact

For interviews, comments or material not on this page, use the contact form and start the message with "Press". We reply by email.

Contact us